What is SASE? Benefits, SSE and deployment explained
In many organisations, networking and security have developed separately. Branch offices run on SD-WAN or MPLS, remote staff connect through a VPN, web traffic passes through a proxy and SaaS applications are managed from another console. Each tool may work well on its own. Together, they can create overlapping policies, multiple endpoint agents and traffic […]
Attack Surface Management: What it is and how to choose a provider
Security testing often starts with a list of systems to check. A vulnerability scanner works through known IP ranges, while a penetration test follows an agreed scope. Both depend on having a reasonably accurate inventory in the first place. Attack surface management (ASM) helps identify what’s missing from that list. It looks for internet-facing systems […]
Supply chain risk: Stop asking, start seeing
You send the supplier questionnaire. A few weeks later it comes back with every box ticked: patching up to date, multi-factor authentication everywhere, systems monitored. You file it, and everyone gets back to work. Most suppliers answer in good faith, but a questionnaire is a snapshot of what they knew on the day they filled […]
“Trust Can No Longer Be Assumed”: 5 Minutes With… Darren James, Senior Product Manager at Specops
We speak to Darren James, Senior Product Manager at Specops, about the growing importance of trust throughout the identity lifecycle, the need to secure human and non-human identities, and why AI will continue to dominate the cybersecurity agenda in 2027. Darren also discusses the opportunities AI presents for strengthening security, the challenges of keeping pace with […]
“Standing Still Is Not a Viable Security Posture”: 5 Minutes With… Andy Hornegold, Chief Security Technologist at Intruder
In the latest instalment of our 5 Minutes With… series, we speak to Andy Hornegold, Chief Security Technologist at Intruder, about the growing influence of AI on the cyber threat landscape, why supply chain attacks will remain a major concern in 2027, and how continuous testing could fundamentally change the way organisations approach security. Andy also shares his […]
Everything you’ve put online. Even the bits you forgot.
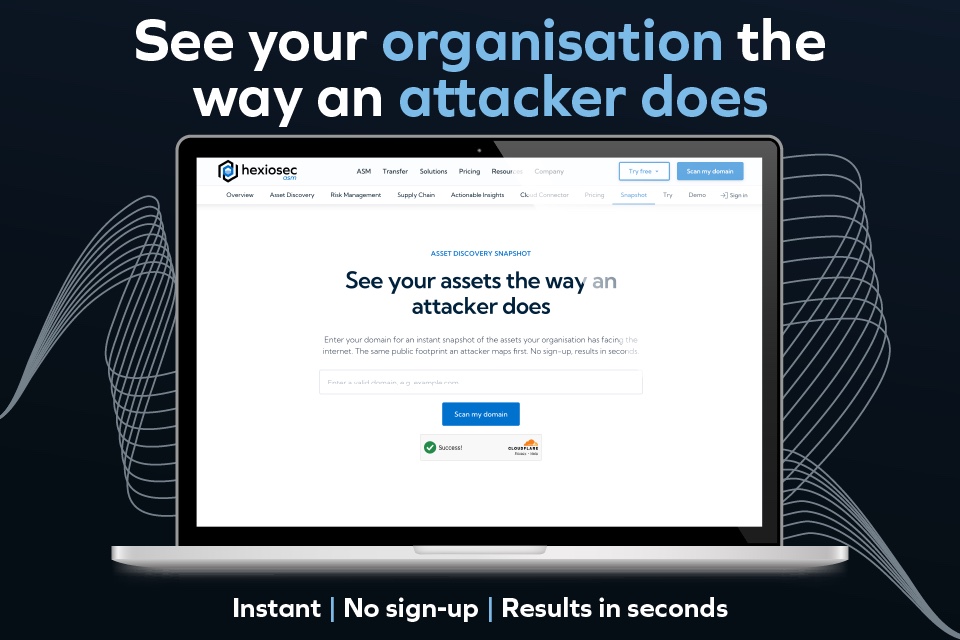
Most IT teams can list the systems they built. Fewer can list everything that is actually reachable from the internet; The subdomain from an old campaign, the test server someone meant to switch off, the mail settings that drifted after a migration. That gap isn’t a failing. It’s what happens when an estate grows faster […]
FinOps and Cloud Cost Management Tools: A Buying Guide
The cloud bill arrives, but nobody can say with confidence which product, team or customer generated a third of the cost. Forecasts drift, spending exceeds expectations and finance asks questions that engineering cannot answer from the console. FinOps and the cloud cost management tools that support it help close that gap. This guide explains what […]
SD-WAN Explained: Managed vs Self-Managed Options
Many multi-site networks were built around a time when most business applications ran in the organisation’s own data centre. MPLS circuits connected branches to headquarters, where traffic could reach the systems employees needed. That hub-and-spoke model made sense at the time. But with more work now taking place in SaaS platforms, public cloud services and […]